For your practice

Cybersecurity for practices that cannot afford downtime.

You run on client records, patient files, schedules, billing, email, and trust. If those systems go down, the work stops. Obsidian Ridge gives small professional practices managed detection, identity protection, and plain-English security guidance — without adding another dashboard your team has to watch.

Aligned with
HIPAAPCI-DSS
CISSP-led • Senior practitioner on every engagementHuntress Partner

TL;DR

What Obsidian Ridge does, who it serves, what it costs.

Managed cybersecurity for small professional practices — law firms, dental and medical offices, accountants, consultants — that depend on email, records, scheduling, billing, and devices staying available and private.

Pricing, per month:

  • Ridge Core, $25 per person: every computer and every email login watched by Huntress’s 24/7 SOC.
  • Ridge Plus, $50 per person: adds the awareness program, email protection and a secure browser for your work apps. This is the tier to look at: it covers the controls cyber insurance applications ask about, including business email compromise.
  • Ridge Reserve, $70 per person: adds the incident response plan, access reviews and patch reporting carriers ask about.

Log collection is Ridge Log, an add-on on any tier.

The difference is one accountable lead running the program for you, not a portal you have to learn.

Island Enterprise Browser

A secure browser for your work apps.

Keep control of work data, on company and personal computers.

Your practice software keeps running exactly as it does today. Island Enterprise Browser only changes the browser, so NetDocuments, iManage and an on-premises document management server are untouched, and the web apps your team already uses — the ones this adds policy to — open the way they always have.

Included in Ridge Plus. No separate price.

Also included in Ridge Reserve.

An everyday decision

A staff member downloads a confidential client file to a home laptop.

Set the rule for each app: allow, watermark or block the action.

  • Copy
  • Paste
  • Download
  • Upload
  • Print
  • Screenshot

Illustrative controls. Rules are configured for your work apps.

The reality

Small practices carry serious data without enterprise security teams.

Law firms, dental offices, clinics, accountants, and consultants all depend on the same fragile set of systems: email, workstations, billing, records, scheduling, and cloud accounts. Attackers know these environments are busy, under-staffed, and rarely watched around the clock. Insurers and regulators are paying attention too.

The risk is not theoretical. One compromised account or infected workstation can interrupt appointments, delay client work, expose sensitive records, and create weeks of cleanup. Obsidian Ridge closes that gap — quietly, without adding another tool your team has to manage.

Pricing

Service Plans

Prices in USD · per person

Tier 01 · Ridge Core

Ridge Core

$25/ person / mo

A shared computer with no named user counts as one person.

Month-to-month · no minimum

Every computer and every email login watched by Huntress's 24/7 SOC, with analysts reviewing alerts.

What's included

  • Always-on protection on every computer in your practice.MDR / EDR: suspicious activity on workstations is watched 24/7 by Huntress's SOC, so one compromised laptop is less likely to interrupt client work.
  • Human review before alerts reach you.SOC triage: a real analyst reviews suspicious activity first, so your team is not expected to interpret raw security alerts during a busy day.
  • Quarterly review of how your security is holding up.Posture review: we look at what changed, what improved, and what still needs attention before small gaps become expensive problems.
  • Direct email support from a senior analyst.Security advisory: you have a person to ask when something feels off, instead of being routed into a generic ticket queue.
  • Add or remove devices at any time.Agent-based deployment: coverage can follow the computers your practice actually uses without locking you into unused seats.
  • Email and cloud account monitoring.ITDR: Microsoft 365 or Google Workspace accounts are watched for break-in attempts and identity-based attacks.
  • Automatic software updates.Patching: software updates are installed automatically on your business computers. We confirm the supported software and update schedule with you during setup.

Replaces or complements

  • Antivirus subscriptions that flag everything and stop nothing
  • Generic IT-installed protection with no one reviewing alerts
  • Monthly log review your team never finds time for
Cyber insurance baselineSOC 2 readinessHIPAA Security Rule

Tier 03 · Ridge Reserve

Ridge Reserve

$70/ person / mo

Annual term · billed monthly

Ridge Plus, plus more of what carriers ask about: a written incident response plan with a yearly ransomware tabletop, quarterly admin-access reviews, and monthly patch reporting you can put on an application.

Everything in Ridge Plus, plus

  • An incident response plan, and a ransomware tabletop every year.IR plan + tabletop: a written plan your team can follow, reviewed each year, and a walkthrough of a ransomware attack before the pressure is real.
  • Quarterly admin-access review.Privileged access: every quarter we check who holds admin rights and whether they still should, and that admin accounts stay separate from everyday ones.
  • Monthly patch report, with a 14-day deadline for known-exploited vulnerabilities.Patch reporting: every vulnerability in CISA's Known Exploited Vulnerabilities catalog is remediated, mitigated, or documented as an exception you accept, within 14 days of CISA listing it. Fourteen days is the longest deadline CISA's current directive, BOD 26-04, gives federal agencies for a catalogued vulnerability. It does not apply to private businesses; we use it as the benchmark.
  • Microsoft 365 security settings applied and kept in place.Managed ISPM for Microsoft 365: Microsoft 365 only. The recommended identity settings are applied on a schedule we agree with you, and a managed setting that someone changes is put back.
  • Your insurance questionnaire, refreshed every year.Questionnaire refresh: the Readiness Sprint's evidence pack, updated each year so your renewal answers stay true.

Replaces or complements

  • An incident response plan that lives in a drawer
  • Patching nobody reports on until the renewal asks
  • A patchwork of security tools that don’t talk to each other
Cyber insurance baselineSOC 2 log retention with the log-collection add-onSupports HIPAA and PCI-DSS evidence
From $25 / person / moStart with Ridge Core
Request a free review

Pricing reflects starting rates. Final pricing depends on environment complexity, number of users, and chosen options. Setup is separate and disclosed up front: $500 for up to 25 machines, $1,000 for 26 to 100.

Centralized security visibility

When the auditor asks, the answer is already stored.

See what's happening across every layer of your practice — without dashboards your team has to learn.

Most small practices run security tools that work in isolation — a firewall here, endpoint protection there, identity for logins, cloud accounts you forgot you connected. When something goes wrong, the evidence is scattered across five different systems, and nobody on your team has time to piece it together.

With Ridge Log, an add-on on any tier, we connect your existing security tools (firewall, endpoint agents, identity providers, cloud accounts) into one place we watch. A SIEM collects security records from your tools so we can investigate activity and produce evidence when insurers, auditors, or clients ask.

Behind the scenes, the Huntress 24/7 SOC reviews the data. In front of you, a written monthly report in plain English — what we observed, what we investigated, what you should know.

What you get

  • One view across your firewall, devices, identity systems, DNS filtering, and cloud accounts
  • 24/7 monitoring by Huntress's SOC behind the scenes
  • A monthly summary in plain English — what we saw, what we did, what you should know
  • Evidence that supports cyber-insurance, SOC 2, HIPAA, and PCI-DSS logging requirements
  • No new dashboards for your team. We watch; you get the summary.

What this replaces or complements

  • Standalone log-management platforms (Splunk, Datadog, Microsoft Sentinel)
  • Managed SOC services from larger MSSPs
  • Internal log review your team isn't doing because they don't have time
  • Reactive-only security where threats are noticed after the fact

Integrations grid

Works with what you already have.

Firewalls

SonicWallFortinet FortiGatepfSenseWatchGuardCisco MerakiSophosPalo Alto NetworksBarracuda CloudGenCisco Secure Firewall ASACisco FirepowerArista NGUbiquiti

Endpoints

Windows Event LogsLinux Event LogsSyslog

Identity

Cisco Duo1PasswordBitwardenLastPassKeeper

DNS Filtering

DNSFilterCisco Umbrella

Cloud

Microsoft AzureAWS CloudTrailAWS S3

Cloud Security

Wiz

RMM

NinjaOne

Infrastructure

Cloudflare

Generic

HTTP Event Collector for custom integrations

Ridge Log, an add-on on any tier • $8 per data source per month. We count your sources with you before we quote.

Request a free review
What makes this different

Built for practice owners, not security buyers.

Real partnership, not a portal.

A dedicated security practitioner who knows your practice — not a ticketing system and a faceless team.

Enterprise tools at small-practice prices.

Managed detection, identity threat detection and training on the Huntress platform, priced for a small practice.

Built for the audits you'll face.

Whether it's HIPAA, SOC 2, your state bar, or a client security questionnaire, the program produces the evidence and controls you'll need.

Who this is for

Is this for your practice?

  • You run a professional practice with 5 to 200 staff — clinic, law firm, dental office, accounting firm, consultancy, or similar
  • You don't have a dedicated internal security person
  • You're seeing more cyber-insurance questions, HIPAA / state-bar / industry compliance pressure, or client security questionnaires
  • You've had a scare — a phishing email, a ransomware threat, an account that got hacked — and you don't want to relive it
  • You want to know your practice is protected without becoming a cybersecurity expert yourself

How It Works

How does this work?

01

Discovery call.

A 30-minute conversation to understand your practice, your concerns, and what you actually need.

02

Scoped proposal.

A clear written proposal with pricing, scope, and timeline — no hidden fees.

03

Onboarding.

Tools deployed, accounts onboarded, baseline established. Most practices are fully running within 2–4 weeks.

04

Ongoing operation.

24/7 Huntress SOC monitoring, monthly reports in plain English, and a person to call when something feels off, with calls returned within one business day.

Honest fit check

Who this is not for

Obsidian Ridge is the right fit for most professional practices. It is not the right fit if any of the following describe you:

  • You want a ticket-only IT provider that responds to your tickets but never tells you what to do.
  • You're looking for a one-time PDF report you'll file and forget. Buy a consultant.
  • You already have an in-house security team and just need someone to procure tools. Buy a tool reseller.
  • You expect cybersecurity to be a checkbox you do once. It's a practice, not a purchase.

If any of those describe you, we'll tell you on the triage call and point you somewhere that fits better. No hard feelings.

FAQ

FAQ

What size practices do you work with?

Sweet spot is 5–200 staff. Below 5, the Ridge Watch personal tier may be a better fit. Above 200, custom engagements are available.

Do you work with HIPAA-covered practices?

Yes. Medical, dental, and behavioral-health practices are core clients. The program produces the evidence the HIPAA Security Rule asks for and aligns with what insurers and auditors expect to see.

What about state-bar or other professional rules?

We work with law firms held to state-bar confidentiality and reasonable-care obligations, accounting firms under professional standards, and consultancies with client confidentiality clauses. We explain where each rule actually intersects with the technical work.

What if we already use other security tools?

Existing tools are evaluated during onboarding. In most cases, what you already pay for gets integrated rather than replaced.

How are payments structured?

Monthly billing, invoiced in advance. Annual prepay discount available. Most practices commit to 12-month terms once they're past Ridge Core.

What happens during an incident?

Two things happen on two different clocks. The Huntress 24/7 SOC detects and triages continuously and can contain an affected device without waiting for business hours.

Everything past containment — investigation, coordination, and talking to you — is ours, and we pick it up within one business day.

A contained device stays contained until we review it, which is the point: the containment is holding while it waits.

Are you a reseller or a service provider?

Both. The security platforms are licensed through partnerships; the service wrapped around them — strategy, response, compliance, executive reporting — is delivered directly. One accountable point of contact.

Do you sign mutual NDAs and MSAs?

Yes, both are standard before any engagement begins.

Not sure if we're a fit?

Free 20-minute triage call

Not ready for a full briefing? Book a free 20-minute triage instead. We confirm fit, scope, and whether you actually need us — or something simpler. No follow-up sequence if it's not a match.

Request a free review

Ready to scope it

Request a free review

Every practice has different needs, risks, and budgets. The best way to find out if this is a fit is a 30-minute discovery call — no commitment, no pressure.

Request a free review

Recently published

What should you read before a discovery call?

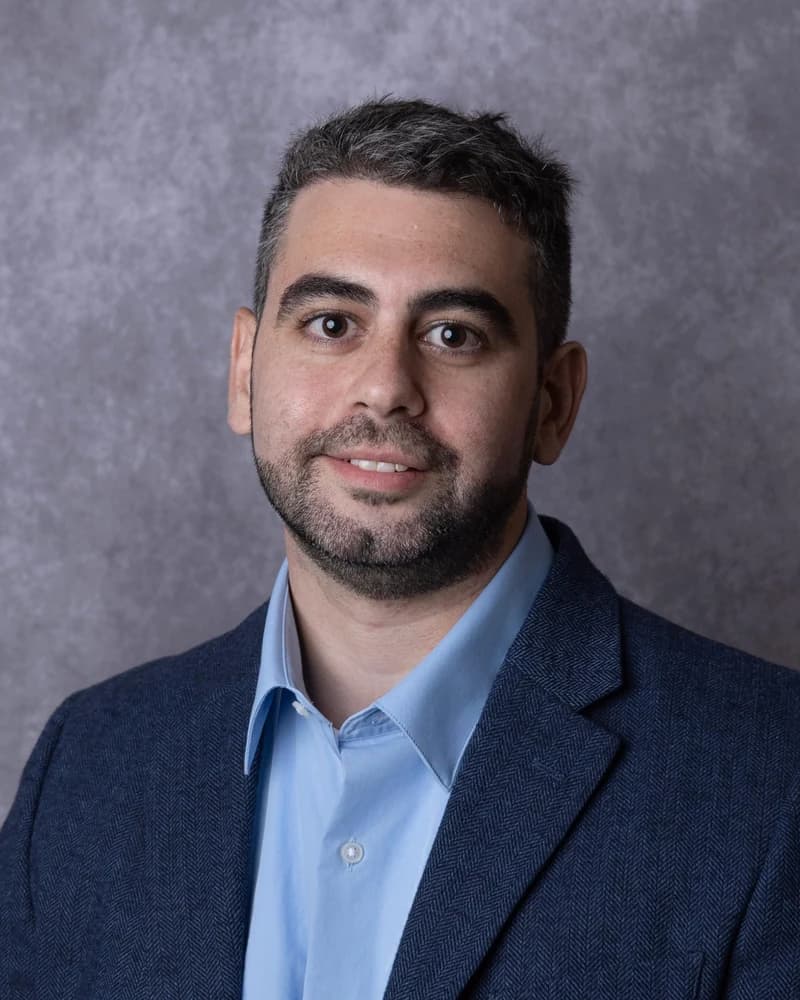
Kfir Yair, founder of Obsidian Ridge

Obsidian Ridge

A practitioner-led service model

Our founder brings a decade of cybersecurity experience in security operations and compliance audits. We give small practices the same defense capability enterprises have — without the enterprise price tag or dashboards no one has time to use.

Obsidian Ridge · CISSP-led cybersecurity